

Every dedicated server has a ceiling. No matter how powerful the CPU or how much RAM you throw at it, there's a traffic level where one machine simply can't keep up on its own. Load balancing is how you get past that ceiling — not by making one server bigger, but by spreading traffic across several servers working together.
Quick answer: A load balancer sits in front of your servers and decides which one handles each incoming request. Instead of all your traffic hitting a single machine, it's spread across multiple servers — so if one gets busy (or fails), the others pick up the slack. This is how sites and applications handle millions of visitors without any single server buckling under the load.
What Is Load Balancing, in Plain Terms?
Picture a busy shop with only one checkout till. Every customer, no matter how many there are, has to queue at that one till. Add a second till, and a person directing customers to whichever till is free, and the queue moves twice as fast.
A load balancer is that person directing customers. It's a piece of software (or sometimes dedicated hardware) that sits between your users and your servers. Every request — a page load, an API call, a file download — passes through it first, and it decides which backend server should actually handle it.
The servers behind the load balancer are usually called a server pool or backend pool — a group of identical (or near-identical) servers all capable of handling the same requests.
Why a Single Server Eventually Hits a Wall
There are two ways to handle more traffic:
Vertical scaling — making one server bigger (more CPU cores, more RAM, faster storage). This works, up to a point, but there's always a ceiling, and it comes with a single point of failure: if that one server goes down, everything goes down with it.
Horizontal scaling — adding more servers instead of making one bigger. This is where load balancing comes in. It has no hard ceiling (you can keep adding servers), and it removes the single point of failure — if one server dies, the others keep serving traffic.
Most serious infrastructure eventually moves to horizontal scaling, because it's more resilient and, past a certain size, actually cheaper than buying increasingly expensive high-end hardware for one machine.
How Load Balancers Actually Decide Where Traffic Goes
Load balancers work at different levels of the network, and it matters which one you're using:
Layer 4 load balancing works at the network/transport level — it looks at IP addresses and ports, and forwards traffic without inspecting what's actually inside it. It's fast and simple, but "dumb" in the sense that it can't make decisions based on the content of a request.
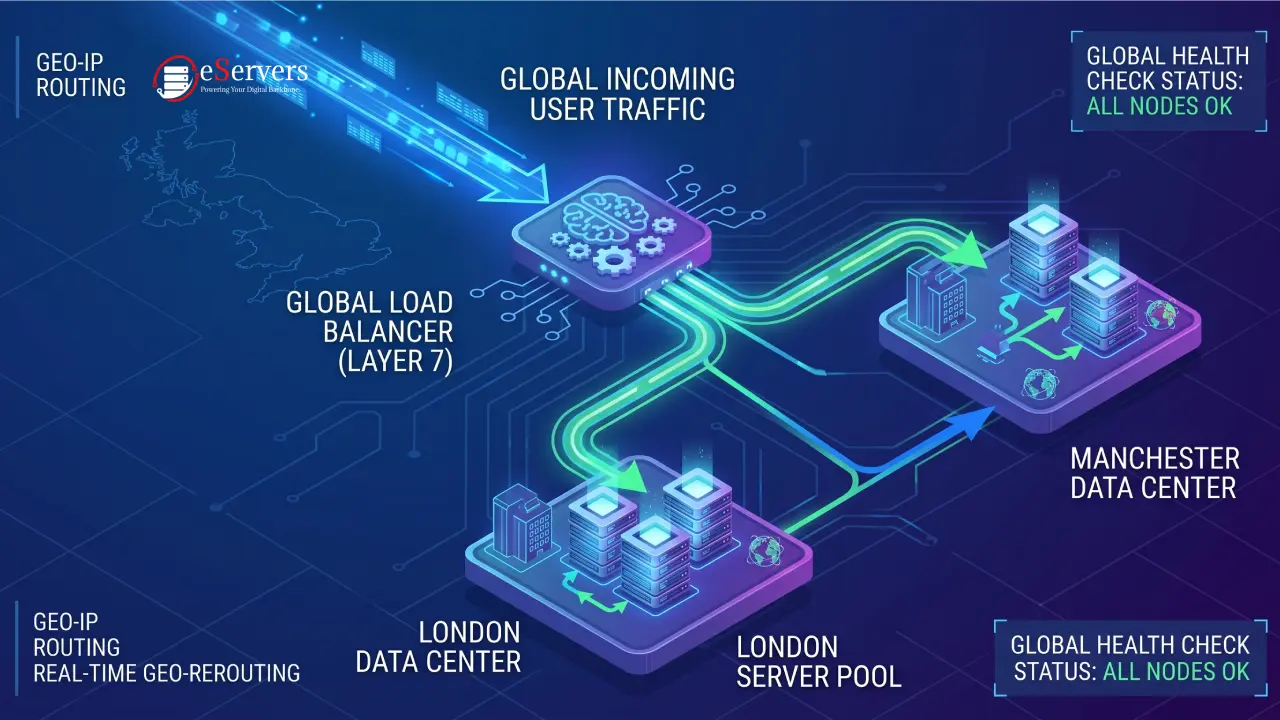
Layer 7 load balancing works at the application level — it can actually read the request (like a web page URL or an HTTP header) and make smarter routing decisions, such as sending all
/api/traffic to one set of servers and/images/traffic to another. This is more flexible but requires more processing power.
Within either type, the load balancer needs a rule for which server gets the next request. Common methods:
Round robin — requests are handed out to servers in turn, one after another, like dealing cards.
Least connections — the request goes to whichever server currently has the fewest active connections, which is smarter when requests take varying amounts of time to process.
IP hash — the same user's IP address always gets sent to the same server, which is useful when you need a user's session to stay on one specific machine.
Common Load Balancing Setups
Active-active — every server in the pool is live and actively handling traffic at the same time. This gives you the most capacity, since nothing sits idle.
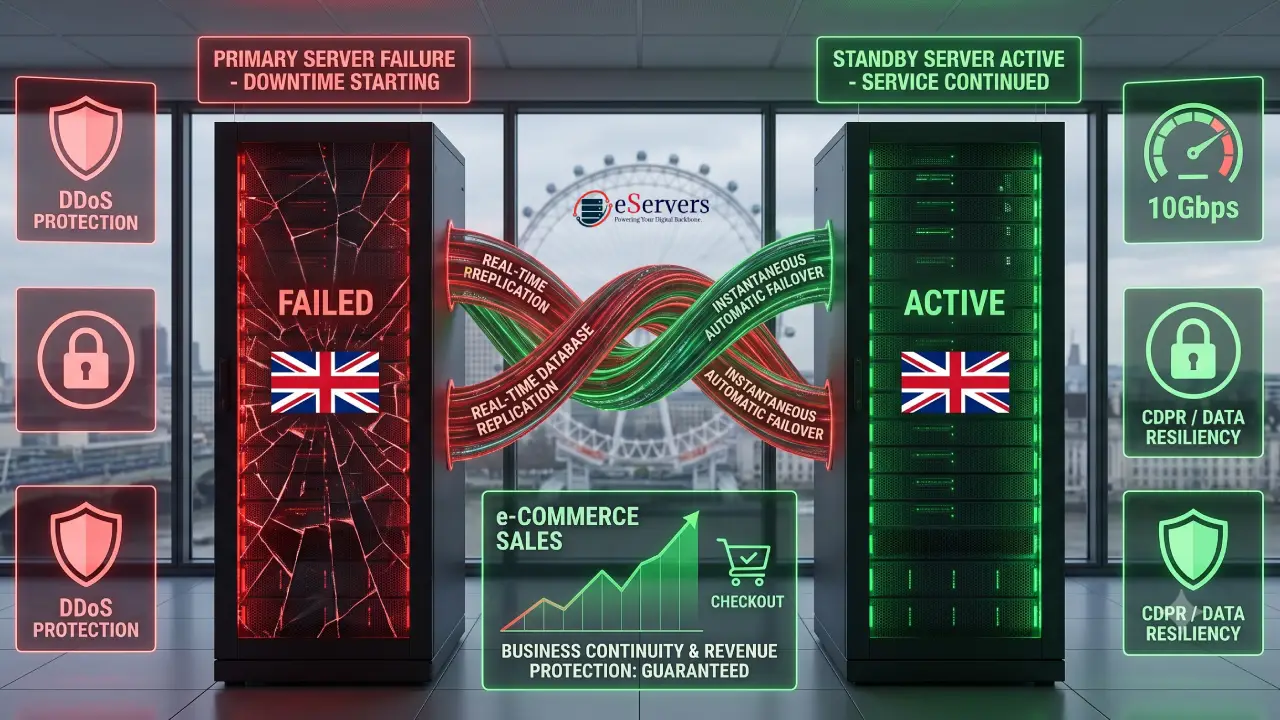
Active-passive — one server handles all the traffic, while a second, identical server sits on standby, ready to take over immediately if the first one fails. This prioritises reliability over raw capacity — you're paying for a backup, not extra throughput.
DNS-based load balancing — instead of one load balancer directing traffic, DNS itself returns different server IP addresses to different users. It's simple to set up but far less precise: it can't react instantly to a server going down, and it can't balance load intelligently based on actual server health.
For most production setups, a dedicated load balancer (software or hardware) sitting in front of an active-active pool gives the best mix of performance and reliability.
Software Load Balancers You'll Actually Use
You don't need special hardware to load balance — two open-source tools handle the vast majority of real-world setups:
Nginx — originally a web server, but very commonly used as a load balancer too. Easy to configure, well-documented, and often already running in your stack anyway.
HAProxy — built specifically for load balancing and proxying traffic. It's the more feature-rich, performance-focused option when load balancing is your main requirement rather than a side feature.
Both are free, open-source, and run comfortably on a standard Linux dedicated server — you don't need to buy expensive dedicated hardware to get started.
A Basic HAProxy Example
Here's a minimal HAProxy configuration that spreads traffic across two backend servers using the "least connections" method:
frontend http_front
    bind *:80
    default_backend web_servers

backend web_servers
    balance leastconn
    server web1 10.0.0.11:80 check
    server web2 10.0.0.12:80 check
A quick breakdown of what's happening:
frontenddefines where incoming traffic arrives (port 80, standard web traffic).backendlists the actual servers handling requests, with their internal IP addresses.checktells HAProxy to continuously test each server's health — more on that next.
This is intentionally simple. Real production configs add SSL, health check tuning, and often Layer 7 rules — but this is the working core of it.
Health Checks and Failover
A load balancer is only useful if it actually knows when a server is unhealthy. Health checks are small, automated tests — usually a request to a specific URL, or just checking if the server responds at all — run every few seconds against each backend server.
If a server fails its health check, the load balancer automatically stops sending it traffic (this is failover) until it starts passing checks again. This is what makes horizontal scaling actually reliable: a server can crash, restart, or need maintenance, and users never notice, because traffic simply routes around it.
SSL Termination
When your site uses HTTPS, someone has to handle the encryption and decryption work. SSL termination means the load balancer itself handles this, then talks to the backend servers over plain, unencrypted HTTP internally (safe, since that traffic never leaves your own private network).
This has a real performance benefit: your backend servers spend their CPU cycles serving actual requests instead of doing encryption work, and you only need to manage SSL certificates in one place — the load balancer — rather than on every server.
Session Persistence (Sticky Sessions)
Some applications need a user's requests to keep landing on the same backend server — for example, if a shopping cart is stored in that server's memory rather than a shared database. This is called session persistence or sticky sessions, and it's usually done with a cookie the load balancer sets, or with the IP hash method mentioned earlier.
Where possible, it's better to design applications to store session data somewhere shared (like a database or Redis cache) rather than relying on sticky sessions — it keeps every server truly interchangeable, which makes scaling and failover simpler.
What Your Infrastructure Actually Needs for This to Work
Load balancing only performs as well as the infrastructure underneath it. A few things matter more than people expect:
Multiple physical servers, not one big one. The entire point is redundancy and horizontal capacity — this only works with genuinely separate hardware. A bare-metal server setup, where each machine has 100% of its own dedicated hardware with zero shared tenancy, avoids the "noisy neighbour" problem you'd get from splitting one physical machine into virtual instances that still compete for the same underlying resources.
Enough network bandwidth between the load balancer and your backend servers. If your load balancer becomes the bottleneck, you haven't actually solved anything. eServers UK offers dedicated servers with network options ranging from standard 1Gbps up to 100Gbps for genuinely high-throughput setups, which matters once you're running real traffic volume between multiple nodes.
Low latency between servers, particularly if they're spread across multiple locations. eServers UK's UK-wide network — with major hubs in London and Manchester offering direct carrier-neutral access to internet exchanges — is built for exactly this kind of low-latency, high-availability setup.
DDoS protection at the network edge. A load balancer improves resilience against normal traffic spikes, but a genuine DDoS attack needs to be filtered before it even reaches your servers. eServers UK includes DDoS mitigation up to 250Gbps as standard across its dedicated server range.
Redundant power and cooling in the data centre itself, so a facility-level issue doesn't take out your whole pool at once. eServers UK's UK data centres run N+N redundant power and N+1 climate control, which matters if your load-balanced servers are physically sitting in the same facility.
Scaling Beyond Just the Web Layer
Load balancing solves traffic distribution, but it's usually only one piece of a larger scaling picture. As you grow, these typically follow:
Database replication — your database often becomes the next bottleneck once web traffic is balanced, since multiple web servers still frequently share one database.
A CDN (Content Delivery Network) — for static files (images, CSS, JavaScript), a CDN caches content closer to users geographically, reducing the load that ever reaches your servers at all.
Caching layers (like Redis or Memcached) — storing frequently requested data in fast memory rather than recalculating or re-querying it on every single request.
Load balancing is the foundation these other layers build on — there's little point optimising your database or adding a CDN if a single web server is still your bottleneck.
Frequently Asked Questions (FAQ)
Do I need a load balancer if I only have one server?
No — load balancing only makes sense once you have two or more servers to distribute traffic across. With a single server, focus on optimising that server's performance first.
Is load balancing the same as a CDN?
No. A CDN caches and serves static content from locations near your users, reducing traffic to your servers. A load balancer distributes the traffic that does reach your servers across multiple machines. They solve different problems and are often used together.
Can I load balance across servers in different physical locations?
Yes, though latency between locations becomes more important the further apart they are. This setup is often called geo-distributed load balancing, and it also improves resilience — an issue at one location doesn't take your whole service down.
Should I use Nginx or HAProxy?
Both work well. Nginx is a good choice if you're already using it as a web server and want load balancing as an added feature. HAProxy is generally preferred when load balancing and traffic management is the primary job, thanks to its more advanced health-checking and routing features.
How many servers do I actually need to start load balancing?
Two is the practical minimum — one alone isn't load balancing, it's just a single server with a proxy in front of it. Two active servers already gives you both extra capacity and basic failover protection.
Final Thoughts
Load balancing turns a single point of failure into a resilient, scalable system — but it depends on solid infrastructure underneath it. Explore eServers UK's bare-metal dedicated servers across UK locations to build a server pool with the bandwidth, low latency, and redundancy a proper load-balanced setup actually needs.
Discover eServers Dedicated Server Locations
eServers provides reliable dedicated servers across multiple global regions. Whether you need low latency, regional compliance, or proximity to your audience, our wide geographic coverage ensures the perfect hosting environment for your project.